Your Network Is Holding You Back.
A global packaging systems manufacturer with about 200 employees and offices in North America, Europe, and South America had patchy connectivity, no Zero Trust controls, and a small IT team. Here's how Loom Security and CINQUE gave them identity-based access at every site, managed end to end.
Customer name withheld at the customer's request.
Does this sound like your environment?
Three continents. One small IT team. A headquarters and remote sites that never connected the same way twice.
Access was broad and ungoverned. It didn't care what role you had. Endpoint protection was out of date. And there wasn't time to fix any of it without slowing down production.
- Fragmented connectivity across headquarters and remote sites
- No Zero Trust controls: access was broad, ungoverned, and role-blind
- Outdated endpoint protection leaving devices and users exposed
- Limited IT resources to modernize without disrupting operations
The real cost of staying still
- Every unmanaged remote site is a possible way in
- With broad access, one compromised account can move freely
- Cyber insurers are tightening Zero Trust and endpoint requirements
- Aging infrastructure quietly wears down performance and adds risk
- Your team can't protect what it can't see or manage consistently
Zero Trust needs a map of who should reach what. They didn't have one yet.
Zero Trust from day one, with a map of who needs what
Loom Security came in as an extension of the customer's team. First a roadmap. Then Zero Trust connectivity through Cato Networks. Then CINQUE, to unify the view across the stack and bring persona-driven intelligence to every site and user.
Secure network modernization
A software-defined network through Cato across headquarters and every remote location.
Zero Trust access
Identity-based least privilege, set by persona using Loom's methodology.
Device posture and web protection
Continuous device posture checks and secure web gateway coverage.
End-to-end platform management
Fully managed by Loom, so the internal team can focus on the business.
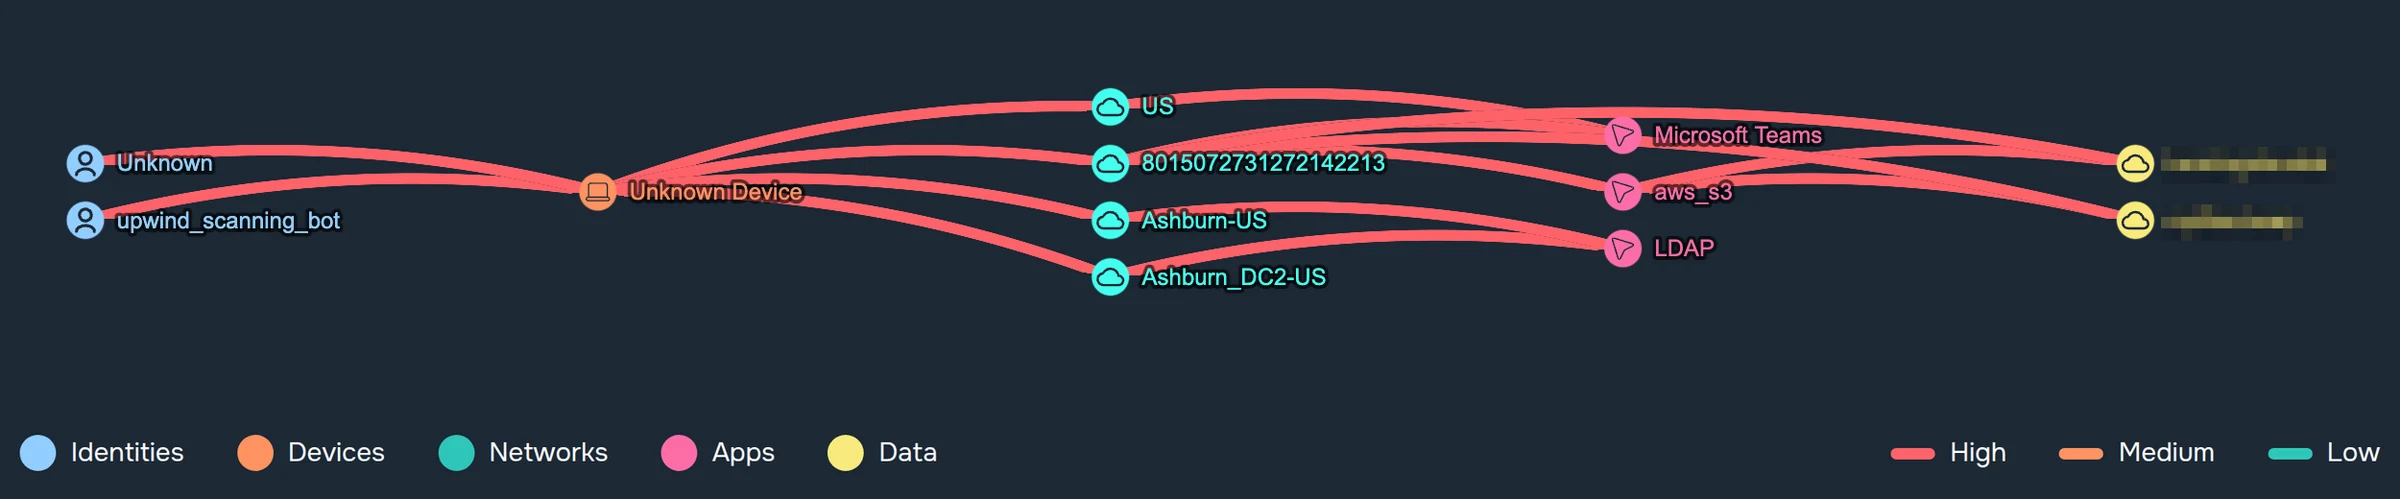
Access that follows what each persona needs
Most mid-size manufacturers know Zero Trust matters. What's missing is a map of who needs what. Personas give you that map.
Get your own map of who needs what
Send one export from your identity provider. In a Persona Discovery Workshop, our team walks you through the personas CINQUE finds, and the people, service accounts, and AI agents that don't fit.